


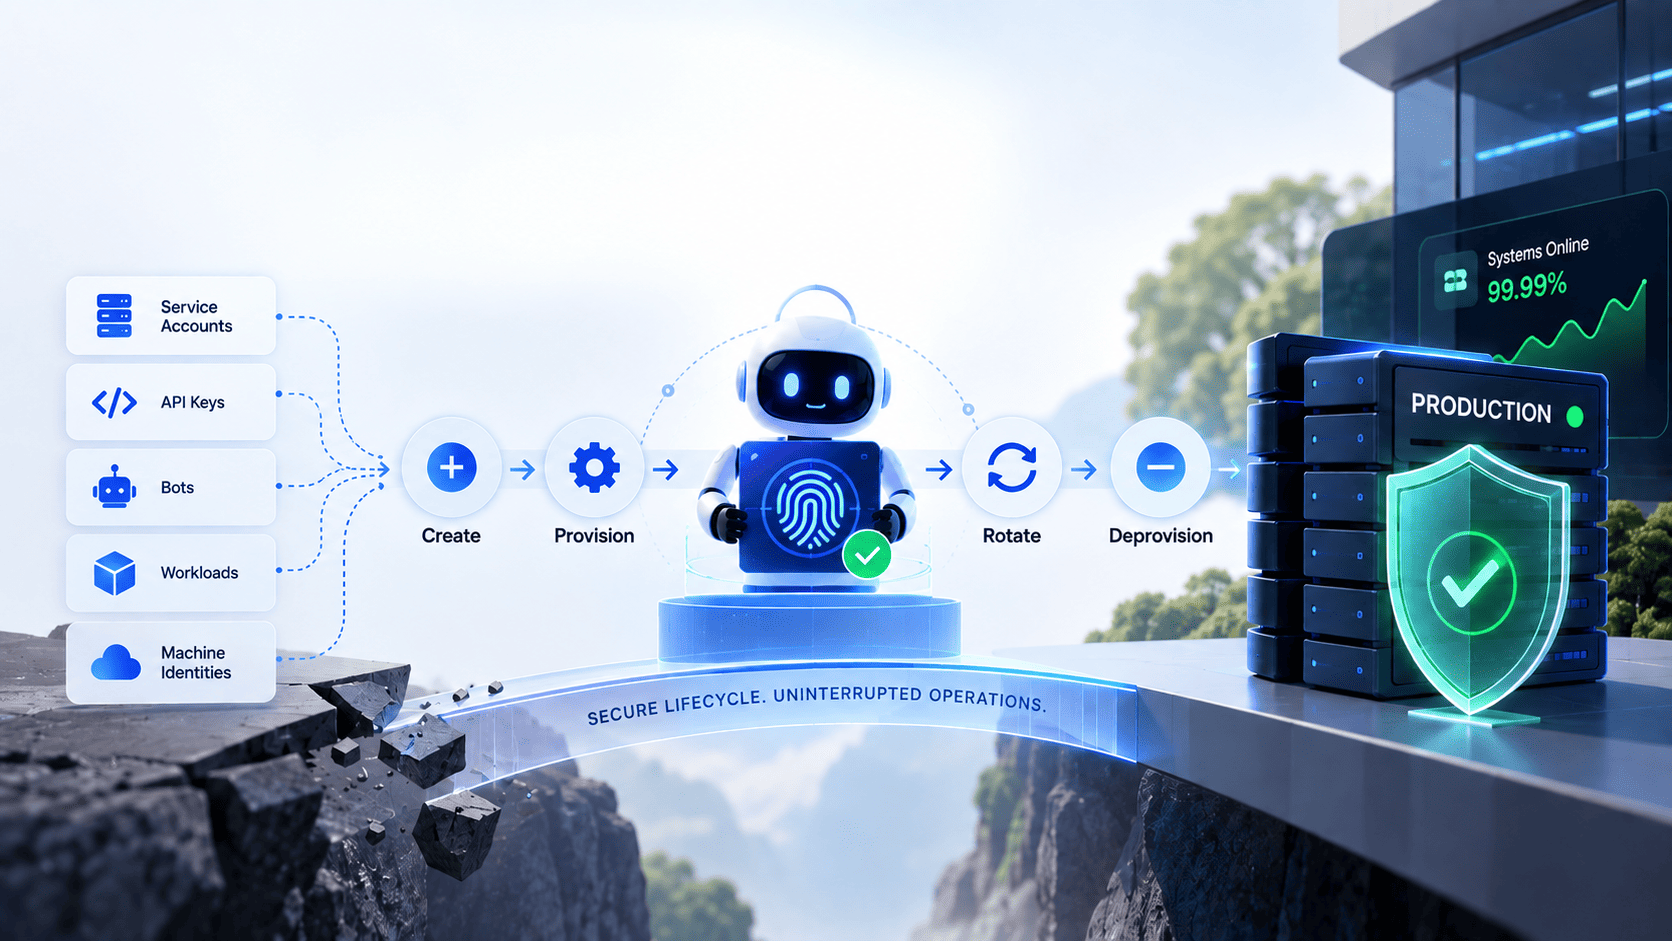

Proper non human identity lifecycle management is essential because unlike human workers, machine accounts often stay active for years without supervision.
Teams must assign clear owners track credentials from creation through usage and implement automated rotation. Without these controls service accounts and API keys accumulate excess access which leads to severe security gaps and unexpected system outages.
Why the Non Human Identity Lifecycle Fails Where the Employee Lifecycle Does Not
Managing employees is easier because their lifecycle is clear. A person joins a company and gets the access they need. Their access can change when their role changes. It is also removed when they leave. Non-human identities do not have the same process because proper non human identity management is often overlooked. API keys and service accounts can stay active for years without anyone checking them. This creates security gaps and can also lead to system problems.
Why Non-Human Identities Get Forgotten
Non-human identities are often created for a specific task. The problem starts when that task ends but the identity stays active. Over time teams may forget why the identity exists or who created it. This accumulation leads directly to non human identity sprawl.
- No Exit Process: Employees go through a clear exit process when they leave. Machine identities do not. A service account can stay active even after the project that created it is finished.
- Forgotten Credentials: Developers may create tokens or accounts for quick tasks. These credentials can later remain in code or environment files. After some time nobody may know if they are still needed.
- No Clear Owner: Every machine identity needs a person who is responsible for it. Without an owner nobody may review its access or remove it when it is no longer needed.
The Risks of Unmanaged Identities
The longer a machine identity stays unmanaged the greater the risk becomes. Old accounts can keep access they no longer need. They can also create problems when systems change or credentials are updated. Proper non human identity lifecycle planning helps teams keep track of these access points from start to finish.
- Old Access: A service account may keep high level access long after a project ends. This gives old credentials more power than they need.
- System Failures: An old script may still connect to a database or another service. If its password or protocol becomes outdated it can cause errors or even affect production systems. Through regular credential rotation, teams can prevent these older accounts from becoming active security risks.
- Clear Lifecycle: Machine identities need the same basic control as employee identities. Each one should have an owner and a clear purpose. It should also have a creation date and a review date. Unused identities should expire automatically.
The Six Stages of Non Human Identity Lifecycle Management and Where Each One Leaks
Managing non human identity tasks is a step by step process. Each stage starts with a new risk if it is not handled well. A strong lifecycle helps teams track every identity and keep it safe from creation to removal.
- Request and Provisioning: Problems can start when developers create API keys through scripts or cloud consoles without approval. Security teams may not even know that new credentials exist. A central request process can help track every new identity.
- Authentication and Issuance: Credentials become risky when they are stored in source code or open configuration files. Anyone with access to the code may find them. Secure vaults should be used to store these secrets.
- Authorization and Access: Service accounts often get more access than they need. Developers may give broad permissions to avoid access errors during testing. If the account is stolen it can then cause much more damage.
- Monitoring and Usage: Many machine identities run without proper monitoring. Teams may not know which systems they access or what data they use. Regular tracking can show which identities are active and which ones are no longer needed.
- Rotation and Maintenance: Teams often hesitate to change old passwords or credentials because they worry that doing so might cause problems in production systems. Modern systems make this easier by keeping secrets in a central and secure place, such as HashiCorp Vault or AWS Secrets Manager. They can also use automatic dual-secret rotation, where both the old and new credentials work for a short period. This gives the system enough time to switch to the new credentials without causing downtime or interruptions.
- Decommissioning and Revocation: Old systems may be removed while their credentials remain active. Proper non human identity lifecycle management ensures these orphaned access points are closed for good. Access should be revoked when the related system or service is retired.
Ownership Attribution Is the Gate Everything Else Waits On
Ownership is one of the most important parts of machine identity lifecycle management. Every service account or API key should have a clear owner. When nobody owns an identity it becomes hard to review or remove. This can lead to forgotten credentials and slow incident response.
Why Ownership Matters
A machine identity should always be linked to a team or a specific person. This makes it clear who should manage the identity and who should act when a problem appears, which is a key part of non-human identity lifecycle management.
- Clear Responsibility: Every credential should have an owner. That owner should know why non human identities exist and what they can access.
- Faster Alerts: Security alerts should reach the right person. Sending alerts to old email accounts or large security queues can cause important warnings to be missed.
- Better Incident Response: When a service account shows strange activity the security team should know who to contact. Clear ownership helps the right team respond faster.
Making Ownership a Rule
Ownership should not depend only on people remembering to add it. It should be part of the normal development process. Systems can check ownership before new machine identities reach production to clearly define what is non human identity governance.
- Required Metadata: Every new identity should include an owner and a clear purpose. It should also include an expiry date when possible.
- Pipeline Checks: Development pipelines can block deployments that do not have valid ownership details. This stops unowned credentials before they reach production.
- Build Accountability: When teams know that ownership checks are part of the process they are more likely to manage identities properly. This makes security a normal part of development instead of treating what are non human identities as an afterthought.
What Changes When AI Agents Enter the Lifecycle
AI agents are changing how organizations think about machine identities. Traditional service accounts usually follow fixed rules and access known systems. AI agents can make decisions and choose tools based on the task they receive.
This makes their access harder to predict and creates a need for stronger controls during every step, especially when managing non human identity examples that require dynamic permissions.
How AI Agents Change Access
AI agents do more than run a fixed script. They can write queries and call tools. They can also start new tasks based on what they find. Because their actions can change at runtime their access needs to be checked as the task moves forward through proper nhi management.
- Dynamic Actions: An AI agent may access different systems based on the task. A fixed access policy may not work well when the agent can change its actions.
- Short-Lived Access: Agents should use temporary tokens that expire after a task ends. This limits the damage if a token is exposed.
- Runtime Checks: Access should be checked before an agent takes an action. The system should confirm that the action fits the task and the agent's allowed scope.
Protecting Autonomous Agents
Autonomous AI agents can create unexpected security risks because they can make decisions and perform tasks on their own. These risks are also mentioned in the OWASP Top 10 for LLMs, especially under Excessive Agency and Insecure Plugin Design.
Harmful inputs or prompt injection attacks can trick an AI agent into doing something it is not supposed to do. To reduce these risks, organizations can use strict rules to control the agent’s behavior, check its permissions in real time, and provide temporary tokens that are only valid for a specific task.
This helps keep the agent secure while still allowing it to perform its required functions.
- Behavior Controls: Systems should watch what an agent is doing while it works. An agent that tries to move outside its allowed scope should be stopped right away.
- Detailed Logs: Every important action should be recorded. Logs should show which tools the agent used and what resources it accessed. This helps teams understand what happened after an incident.
- Automatic Response: Security tools should be able to block risky actions and revoke access quickly. This is important because AI agents can work much faster than people can respond.
Building for AI Scale
AI agents can run all day without human help. As more teams use them the number of machine actions can grow very quickly. Manual checks cannot keep up with this speed. Identity systems need to make fast decisions without slowing down normal work.
- Automated Decisions: Identity tools should check risk and access automatically. They should decide if an agent can perform an action before allowing it.
- Real-Time Monitoring: Teams need to watch agent behavior as it happens. Changes in normal activity can help reveal a compromised agent.
- Instant Revocation: If an agent starts acting in a dangerous way its access should be removed at once. Short lived permissions make this easier and reduce the chance of serious damage.
What to Audit in Your Non Human Identity Lifecycle and When
Good identity management needs regular checks. Teams should know which identities are active and what they are doing. Audits should not happen only during a yearly security review. Different checks should run at different times so problems can be found early.
Continuous Activity Auditing
Real time monitoring helps teams see what machine identities are doing right now. It can show unusual activity before it becomes a bigger problem.
- Track Activity: Monitor API calls and token use as they happen. This helps teams spot sudden changes in normal activity.
- Watch for Anomalies: A service account that suddenly sends large amounts of data may be compromised. Real time alerts can help stop the action before more damage occurs.
- Build a Baseline: Learn what normal activity looks like for each identity. Any major change from that pattern should trigger a closer look.
Regular Privilege Reviews
Machine identities should be reviewed on a regular schedule. A weekly or monthly review can help teams find accounts that no longer need their current access.
- Review Active Accounts: Team leads should confirm that each service account still has a valid purpose. Unused accounts should be removed or disabled.
- Reduce Access: Old projects may leave accounts with more access than they need. Regular reviews can remove extra permissions and reduce risk.
- Keep Access Current: As projects change their identity permissions should change too. Regular checks help prevent old access from building up over time.
Post-Deployment and Incident Audits
Major software releases and security incidents can change how machine identities work. A quick review after these events can help teams find problems before they spread.
- Check New Changes: Review access logs after major releases. This can show if a new feature changed how an identity accesses systems.
- Review Incidents: After a security incident check which identities were involved. This helps teams understand what happened and where controls failed.
- Verify Production: Make sure new permissions and integrations match the intended design. This adds an extra layer of protection without slowing down normal releases.
What a Platform Needs to Close the Non Human Identity Lifecycle
What a Platform Needs to Close the Lifecycle
Managing machine identities by hand becomes difficult as cloud systems grow. Teams need a platform that can find identities and track them across the full lifecycle. It should also reduce manual work and make sure every identity has the right access.
- Automatic Discovery: The platform should find API keys and service accounts across cloud systems and code repositories. It should also detect identities created through development pipelines.
- Short-Lived Credentials: Applications should use temporary tokens instead of static keys that stay active for years. Short-lived access reduces the risk if a credential is exposed.
- Fast Revocation: The platform should be able to remove access when an identity goes beyond its allowed scope. This helps stop risky activity before it affects production.
Making Identity Management Easier
A good platform should fit into the way developers already work. Teams should not have to manage large spreadsheets or follow extra manual steps every time they create a new service account.
- Workflow Integration: The platform should work with cloud providers and development tools that teams already use. This keeps identity management part of the normal development process.
- Clear Ownership: New identities should be linked to the right team or engineer. The platform should also set an expiry date so unused identities do not stay active forever.
- Better Visibility: Teams need a simple view of which identities can access which systems. This helps them understand the impact before removing an old credential.
The Business Value of a Dedicated Platform
A dedicated platform can reduce both security risks and production problems. It gives teams a clear view of machine identities and removes many tasks that are hard to manage by hand.
- Fewer Outages: Automated rotation can help prevent old credentials from causing production failures. Teams can keep services running while credentials are updated.
- Lower Security Risk: Every identity can have clear permissions and a defined owner. This makes it harder for stolen or forgotten credentials to create serious damage.
- Better Control: Security teams can track identity activity and compliance from one place. Engineers can also get the access they need without relying on long lived credentials.
Close the Lifecycle Before Your Agent Count Doubles
Machine identities are growing faster than human identities. Every new bot or service can add another account or token to manage. Manual tracking will not work at this scale. Organizations need a simple and proactive way to discover these identities and control them before they become a security or uptime problem.
- Start Before Problems Grow: Do not wait for a breach or major outage. Use automated discovery to find machine identities across cloud systems and development tools. Set clear owners and expiry dates from the start.
- Scale With Your Environment: As applications and AI agents grow the number of machine identities will grow too. Automated tools can track new tokens as they appear and help teams manage them across large cloud environments.
- Prepare for Compliance: Strong identity controls also make audits easier. Every machine identity should have clear access rules and an owner. Activity should be easy to review when needed.
- Improve Daily Operations: Good lifecycle management reduces the time engineers spend fixing broken integrations and old credentials. It also helps security teams keep machine access within least privilege limits. A well managed machine workforce can support growth without adding unnecessary risk.
Managing machine credentials by hand becomes difficult as cloud systems grow. That’s why platforms like Infisign UniFed are important for modern security. By bringing different access systems together, it helps organizations manage credentials, control access, and automate key security tasks across complex digital environments.
- Workforce Identity Management automates the full employee access lifecycle, from onboarding to offboarding. It supports least-privilege access and just-in-time permissions, helping businesses give users only the access they need, when they need it.
- UniFed Customer Identity Management offers passwordless single sign-on, biometric authentication, and a unified identity system. These features make login easier for customers while adding stronger protection against automated bot attacks.
- Decentralized Identity and Verification uses zero-knowledge proofs, secure wallets, and ready-to-use authentication templates. This helps businesses meet compliance needs while keeping personal data more private and secure.
Don’t let old API keys and unused service accounts put your infrastructure at risk. Take control of machine access and see how automated governance can help keep your systems safe. Schedule a personalized demo today.
FAQ
Q. What is non human identity lifecycle management?
A. This practice tracks machine accounts and API keys from creation to removal, enforcing ownership, permission limits, automated rotation, and secure decommissioning to prevent security breaches and system downtime.
Q. What are non human identities and what are some examples?
A. These digital credentials authenticate machines, scripts, and software. Common examples include API keys, database service accounts, CI/CD pipeline tokens, cloud integration secrets, and autonomous software agents.
Q. How often should you rotate API keys and service account credentials?
A. Traditional security guidelines, such as CIS Benchmarks, often recommend changing static keys every 30 to 90 days. Automated dual-secret rotation can be used during this process so that both the old and new keys work for a short time, helping to prevent production systems from going offline.
However, modern security systems are moving away from long-term static credentials. Instead, they use dynamic and temporary tokens, such as Cloud Workload Identity Federation and OIDC. These tokens automatically expire after a few minutes or hours, which reduces the risk of someone misusing old credentials.
Q. What causes non human identity sprawl?
A. Sprawl happens when developers create quick tokens for temporary tasks, leave secrets in code files, assign no clear owners, and forget to remove access after projects end.
Q. Is machine identity lifecycle management the same as non-human identity lifecycle management?
A. Although these terms are often used as if they mean the same thing, Non-Human Identity (NHI) is actually a broader concept. Machine identities usually refer to the technical identities used by systems and infrastructure, such as X.509 certificates, SSH keys, and mTLS.
NHI includes all of these machine identities, but it also covers application-level credentials, such as static API keys, OAuth grants, CI/CD secrets, and autonomous AI agents. In simple terms, machine identities are one part of NHI, while NHI covers a much wider range of non-human access and identities.


